AWS Certified Solutions Architect — Associate (SAA-C03) Domain 1

Design Secure Architectures
Official Exam Guide: https://docs.aws.amazon.com/aws-certification/latest/examguides/solutions-architect-associate-03-domain1.html
Skill Builder: Exam Prep Plan: AWS Certified Solutions Architect — Associate (SAA-C03)
Note: Some Skill Builder labs require a subscription.
How to Study This Domain Effectively
Study Tips
- Don’t memorize service names — understand security boundaries: Focus on understanding who can access what, from where, and under what conditions rather than memorizing feature lists.
- Draw architecture diagrams by hand: Sketch IAM trust relationships, cross-account access patterns, and VPC security architectures on paper to solidify your mental models.
- Practice explaining design decisions out loud: If you can justify why one security approach is better than another (e.g., why roles are more secure than access keys), you’re thinking like the exam expects.
- Connect concepts across services: Security isn’t isolated — understand how IAM policies, security groups, KMS keys, and S3 bucket policies work together in real architectures.
- Focus on the “why” behind best practices: The exam tests whether you understand the reasoning behind security recommendations, not just whether you’ve memorized the Security Pillar whitepaper.
Recommended Approach
- Start with the IAM User Guide’s policy evaluation logic section: Understanding how AWS evaluates permissions is foundational to every other security decision you’ll make.
- Build a mental model of the Shared Responsibility Model: Draw a line between what AWS manages and what you manage for different service types (IaaS, PaaS, SaaS) — this clarifies 20% of exam questions.
- Lab everything you read about: Create IAM roles, configure cross-account access, set up VPC endpoints, and encrypt data with KMS in your own AWS account to cement theoretical knowledge.
- Study service FAQs before taking practice exams: FAQs contain the exact edge cases and comparisons (gateway vs. interface endpoints, SCPs vs. IAM policies) that appear as distractors on the exam.
- Review each domain task by asking “What could go wrong?”: Security questions often present a scenario and ask you to identify the vulnerability or the most secure alternative — train yourself to spot weaknesses.
Task 1.1: Design Secure Access to AWS Resources
Knowledge Areas & AWS Documentation Reading List
1. Access Controls and Management Across Multiple Accounts
Why: Organizations use multiple AWS accounts to isolate workloads, departments, and environments for security, compliance, and billing purposes. The exam tests your ability to design centralized access management across accounts, understand organizational structures, and implement governance at scale. This is critical for enterprise scenarios where you need to manage hundreds or thousands of AWS accounts while maintaining security boundaries and operational efficiency.
AWS Documentation:
- AWS Organizations User Guide
- Best Practices for Organizational Units
- Organizing Your AWS Environment Using Multiple Accounts
2. AWS Federated Access and Identity Services
Why: Modern enterprises already have existing identity systems like Active Directory or SAML providers, and the exam tests whether you understand how to integrate these with AWS rather than creating duplicate user management. You need to know when to use IAM users versus federated access, how IAM Identity Center simplifies SSO across multiple accounts, and how to design identity architectures that scale. Questions often present scenarios where you must choose between different federation approaches based on requirements like centralized user management, temporary credentials, or integration with existing corporate directories.
AWS Documentation:
- IAM User Guide
- IAM Identity Center User Guide
- Tutorial: Delegate Access Across AWS Accounts Using IAM Roles
- Identity Providers and Federation
3. AWS Global Infrastructure
Why: Understanding Regions and Availability Zones is fundamental to designing architectures that meet data residency requirements, comply with regulations like GDPR, and provide fault tolerance. The exam tests whether you know how to distribute workloads across AZs for high availability and select appropriate regions based on latency, compliance, and service availability. This knowledge appears in questions across multiple domains, not just security.
AWS Documentation:
4. AWS Security Best Practices
Why: The exam heavily tests whether candidates follow AWS-recommended security practices, particularly the principle of least privilege, defense in depth, and enabling security features by default. These best practices form the foundation for evaluating security design decisions throughout the exam. You’ll encounter scenarios where you must identify security vulnerabilities in proposed architectures or select the most secure option among multiple valid designs.
AWS Documentation:
- Security Best Practices in IAM
- AWS Security Best Practices Whitepaper
- Security Pillar — AWS Well-Architected Framework
5. AWS Shared Responsibility Model
Why: This is one of the most frequently tested concepts because it clarifies the security boundary between AWS and the customer. Misunderstanding this leads to incorrect answers about who is responsible for patching operating systems, encrypting data, managing network controls, and meeting compliance requirements. The exam tests whether you know that AWS secures the infrastructure while you secure what you put in the cloud.
AWS Documentation:
Skills & Corresponding Documentation
Applying AWS Security Best Practices to IAM Users and Root Users
Why: Root account compromise is catastrophic because it has unrestricted access to everything in the account. The exam tests whether you understand how to secure the root user (enable MFA, delete access keys, use only for specific tasks) and properly manage IAM users with appropriate controls like password policies and MFA enforcement.
AWS Documentation:
- Security Best Practices for Your AWS Root User
- Using Multi-Factor Authentication (MFA) in AWS
- Enable MFA for IAM Users
Designing a Flexible Authorization Model
Why: IAM policy design is central to AWS security and appears throughout the exam. You must understand how users, groups, roles, and policies interact to answer questions about granting appropriate permissions while maintaining least privilege. The exam tests your ability to design authorization models that are both secure and scalable.
AWS Documentation:
- IAM Identities (Users, Groups, and Roles)
- IAM Policies and Permissions
- IAM JSON Policy Reference
- Policy Evaluation Logic
Designing Role-Based Access Control Strategy
Why: IAM roles enable temporary credentials and eliminate long-term access keys, which is essential for security. The exam tests your understanding of how EC2 instances, Lambda functions, and cross-account access work securely using roles, when to use AWS STS for temporary credentials, and how role assumption works — all common exam scenarios.
AWS Documentation:
- IAM Roles
- AWS Security Token Service (AWS STS)
- Using IAM Roles
- Tutorial: Delegate Access Across AWS Accounts Using IAM Roles
- Switching to an IAM Role
Designing Security Strategy for Multiple AWS Accounts
Why: Enterprise organizations require account-level isolation and centralized governance to maintain security at scale. The exam tests whether you understand how to use AWS Control Tower for account provisioning with guardrails, implement SCPs to set permission boundaries across organizational units, and design account structures that support both security and operational requirements.
AWS Documentation:
Determining Appropriate Use of Resource Policies
Why: Resource-based policies (like S3 bucket policies and Lambda resource policies) work differently than identity-based policies, and the exam tests whether you know when to use each type. You need to understand how they interact during policy evaluation and scenarios where resource policies are required, such as cross-account access without role assumption.
AWS Documentation:
- Identity-Based Policies and Resource-Based Policies
- Amazon S3 Bucket Policies
- AWS Services That Work with IAM
Determining When to Federate a Directory Service
Why: Many organizations already have Active Directory or other identity providers, and the exam tests whether you understand when federation makes sense versus creating separate IAM users. You need to know the different federation options (AWS Directory Service, SAML, OIDC) and select the appropriate approach based on requirements like existing infrastructure, user management preferences, and SSO needs.
AWS Documentation:
Task 1.2: Design Secure Workloads and Applications
Knowledge Areas & AWS Documentation Reading List
1. Application Configuration and Credentials Security
Why: Hard-coded credentials in applications are one of the most common security vulnerabilities and a frequent exam topic. The exam tests whether you understand how to use AWS Secrets Manager for automatic rotation of database passwords, AWS Systems Manager Parameter Store for configuration management, and best practices for avoiding long-term credentials. Questions often present scenarios where applications need access to databases or APIs, and you must select the most secure credential management approach.
AWS Documentation:
- AWS Secrets Manager User Guide
- AWS Systems Manager Parameter Store
- Best Practices for Managing AWS Access Keys
2. AWS Service Endpoints
Why: VPC endpoints enable private connectivity to AWS services without internet gateways, which enhances security by keeping traffic within the AWS network and reduces data transfer costs. The exam tests whether you understand the difference between gateway endpoints (S3, DynamoDB) and interface endpoints (most other services), when to use each type, and how they improve security posture. This is a frequently tested security pattern for keeping data private.
AWS Documentation:
3. Control Ports, Protocols, and Network Traffic on AWS
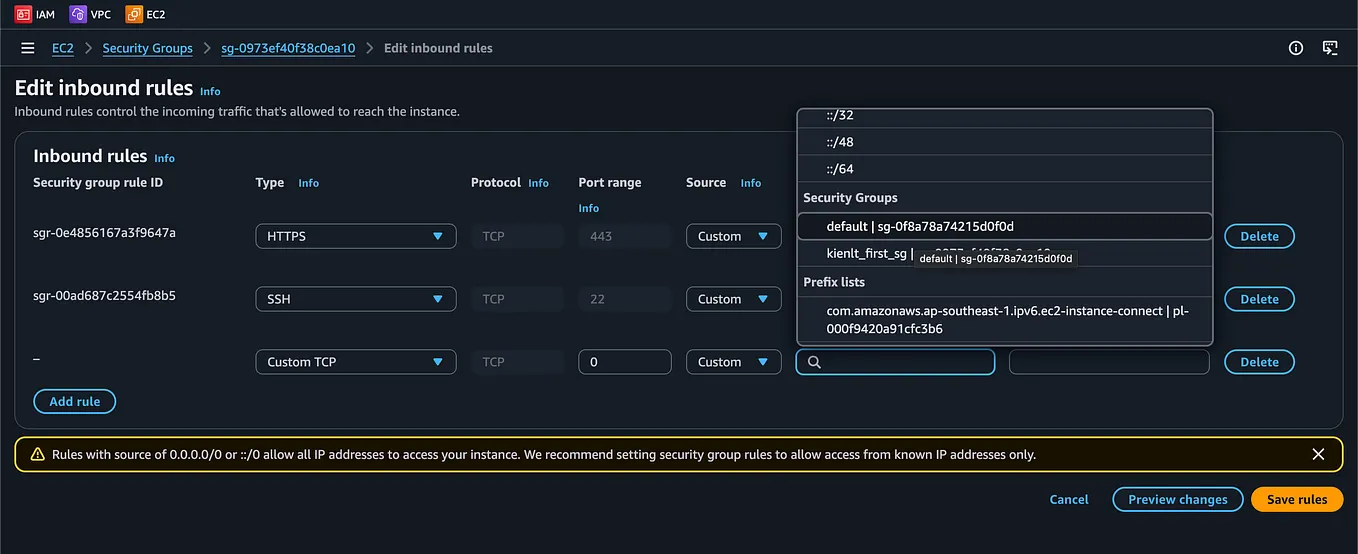
Why: Security groups and network ACLs are fundamental network security controls in AWS, and the exam extensively tests the differences between them. You must understand that security groups are stateful (return traffic is automatically allowed) while NACLs are stateless (you must explicitly allow return traffic), when to use allow-only rules versus deny rules, and how they work together for defense in depth.
AWS Documentation:
4. Secure Application Access
Why: Modern applications require user authentication and authorization, and the exam tests your understanding of Amazon Cognito for managing user identities, user pools for authentication, and identity pools for authorization to AWS resources. You need to know when to use Cognito versus other identity services, how to integrate with Application Load Balancers for authentication, and how to secure communications with SSL/TLS certificates from ACM.
AWS Documentation:
- Amazon Cognito Developer Guide
- Application Load Balancer Authentication
- AWS Certificate Manager User Guide
5. Security Services with Appropriate Use Cases
Why: AWS offers multiple security services with specific purposes, and the exam tests whether you can select the appropriate service for each scenario. You need to know that GuardDuty detects threats through intelligent threat detection, Macie discovers and protects sensitive data in S3, Security Hub provides a comprehensive view of security alerts, and Cognito manages application user identities — each service has distinct use cases that appear in exam questions.
AWS Documentation:
- Amazon Cognito User Pools
- Amazon GuardDuty User Guide
- Amazon Macie User Guide
- AWS Security Hub User Guide
6. Threat Vectors External to AWS
Why: Applications face external threats like DDoS attacks, SQL injection, and cross-site scripting, and the exam tests your knowledge of AWS security services that protect against these threats. You need to understand AWS Shield for DDoS protection (Standard vs. Advanced), AWS WAF for filtering web application traffic with custom rules, and how to design resilient web applications that can withstand attacks — these are common exam scenarios.
AWS Documentation:
Skills & Corresponding Documentation
Designing VPC Architectures with Security Components
Why: VPC architecture is foundational to AWS networking and security. The exam tests your ability to design secure network topologies using security groups for instance-level protection, NACLs for subnet-level protection, route tables for traffic direction, and NAT gateways for outbound internet access from private subnets. You must understand how these components work together to implement defense in depth.
Get Mark Schoonover’s stories in your inbox
Join Medium for free to get updates from this writer.
AWS Documentation:
- Amazon VPC User Guide
- How Amazon VPC Works
- Security Groups for Your VPC
- Route Tables
- Network ACLs
- NAT Gateways
Determining Network Segmentation Strategies
Why: Separating public-facing resources from private backend systems is a core security principle and frequently tested on the exam. You need to understand when to use public subnets (for resources that need direct internet access) versus private subnets (for resources that should not be directly accessible from the internet), and how to enable internet access for private resources securely through NAT gateways.
AWS Documentation:
Integrating AWS Services to Secure Applications
Why: Real-world applications require multiple security services working together, and the exam tests your ability to design cohesive security architectures. You need to know how to combine AWS Shield and WAF for web application protection, use Secrets Manager for credential management, implement IAM Identity Center for SSO, and integrate these services into a comprehensive security strategy.
AWS Documentation:
- AWS Shield Standard and Advanced
- AWS WAF Developer Guide
- AWS IAM Identity Center User Guide
- AWS Secrets Manager User Guide
- Rotating AWS Secrets Manager Secrets
Securing External Network Connections
Why: Hybrid cloud scenarios require secure connectivity between on-premises data centers and AWS, and the exam tests whether you understand when to use Site-to-Site VPN (for encrypted connections over the internet) versus AWS Direct Connect (for dedicated private connections). You also need to know how to configure these securely, when to use AWS Client VPN for remote user access, and how VPN CloudHub enables communication between multiple sites.
AWS Documentation:
Task 1.3: Determine Appropriate Data Security Controls
Knowledge Areas & AWS Documentation Reading List
1. Data Access and Governance
Why: Preventing unauthorized data access and accidental public exposure is critical, especially with S3 buckets which are frequently misconfigured. The exam tests whether you understand IAM Access Analyzer for detecting resources shared with external entities, S3 Access Points for simplifying permission management at scale, and S3 Block Public Access for preventing data leaks. You need to know how these services work together to protect sensitive data and prevent compliance violations.
AWS Documentation:
- AWS IAM Access Analyzer
- Managing Access with S3 Access Points
- Blocking Public Access to Your Amazon S3 Storage
2. Data Recovery
Why: Data loss can be catastrophic for businesses, and the exam tests your understanding of backup and recovery strategies. You need to know how to use S3 versioning to protect against accidental deletions, AWS Backup for centralized backup management across multiple services, and RDS automated backups with point-in-time recovery. The exam presents scenarios where you must design solutions that meet specific recovery time objectives (RTO) and recovery point objectives (RPO).
AWS Documentation:
3. Data Retention and Classification
Why: Compliance regulations often require specific data retention periods and classification levels, and the exam tests your knowledge of automating these requirements. You need to understand S3 lifecycle policies for automatic transitions between storage classes, how to select appropriate storage classes for cost optimization, Amazon Macie for discovering and classifying sensitive data, and S3 Object Lock for compliance requirements like WORM (write once, read many) storage.
AWS Documentation:
- Managing Your Storage Lifecycle
- Using Amazon S3 Storage Classes
- Discovering Sensitive Data with Amazon Macie
- Using S3 Object Lock
4. Encryption and Appropriate Key Management
Why: Encryption is mandatory for many compliance frameworks, and the exam heavily tests KMS concepts. You need to understand the difference between AWS managed keys (created and managed by AWS services) and customer managed keys (you control rotation and policies), when to use each type, how key rotation works, and when to use AWS Certificate Manager for SSL/TLS certificates. This is fundamental to protecting data at rest and in transit.
AWS Documentation:
- AWS Key Management Service Developer Guide
- AWS KMS Concepts
- AWS Certificate Manager User Guide
- Encrypting Data-at-Rest and Data-in-Transit
Skills & Corresponding Documentation
Aligning AWS Technologies to Meet Compliance Requirements
Why: Organizations must meet industry-specific compliance standards like HIPAA, PCI-DSS, and SOC 2. The exam tests whether you understand how to use AWS Artifact to access compliance reports, AWS Config to monitor compliance with rules, and AWS Audit Manager to automate audit preparation. You need to know which AWS services support specific compliance frameworks and how to implement required controls.
AWS Documentation:
- AWS Compliance Programs
- AWS Artifact User Guide
- AWS Config Conformance Packs
- AWS Audit Manager User Guide
Encrypting Data at Rest
Why: Protecting stored data through encryption prevents unauthorized access if storage media is compromised or improperly disposed of. The exam tests how to enable encryption for EBS volumes, S3 buckets using server-side encryption, RDS databases with transparent data encryption, and DynamoDB tables — all using AWS KMS for key management. You must understand that encryption at rest is essential for any secure architecture and is often required for compliance.
AWS Documentation:
- How AWS Services Use AWS KMS
- Amazon EBS Encryption
- Protecting Data Using Server-Side Encryption with Amazon S3
- Encrypting Amazon RDS Resources
- DynamoDB Encryption at Rest
Encrypting Data in Transit
Why: Data transmitted over networks can be intercepted, and the exam tests your knowledge of protecting data in transit using SSL/TLS. You need to understand how to use AWS Certificate Manager to provision and manage certificates, configure HTTPS listeners on Application Load Balancers, enable SSL/TLS for S3 API calls, and configure CloudFront to require HTTPS — ensuring data remains encrypted during transmission between clients and AWS services.
AWS Documentation:
- AWS Certificate Manager User Guide
- Protecting Data Using Encryption in Amazon S3
- Create an HTTPS Listener for Your Application Load Balancer
- Using HTTPS with CloudFront
Implementing Access Policies for Encryption Keys
Why: KMS keys require careful permission management to balance security and usability, and the exam tests whether you understand the different policy types that control key access. You need to know how key policies work (the primary way to control access), when to use IAM policies for KMS, and how grants enable temporary permissions — controlling who can use keys to encrypt/decrypt data, manage keys, and rotate keys.
AWS Documentation:
Implementing Data Backups and Replications
Why: Business continuity requires robust backup and replication strategies, and the exam tests your understanding of different approaches. You need to know when to use AWS Backup for centralized backup management, S3 cross-region replication for disaster recovery, RDS read replicas for both performance and resilience, EBS snapshots for volume backups, and DynamoDB backups for point-in-time recovery — each with different use cases and recovery characteristics.
AWS Documentation:
- AWS Backup Developer Guide
- Replicating Objects in Amazon S3
- Working with Read Replicas for Amazon RDS
- Amazon EBS Snapshots
- Using On-Demand Backup and Restore for DynamoDB
Implementing Policies for Data Access, Lifecycle, and Protection
Why: Organizations need automated data management to reduce costs and meet compliance requirements, and the exam tests your ability to implement these automations. You need to understand S3 bucket policies for access control, lifecycle policies for automatic transitions to cheaper storage classes, S3 Glacier Vault Lock for compliance archives, and S3 Object Lock for immutable storage — these are essential for cost optimization and regulatory compliance.
AWS Documentation:
- Bucket Policies and User Policies
- Setting Lifecycle Configuration on a Bucket
- Amazon S3 Glacier Vault Lock
- Using S3 Object Lock
Rotating Encryption Keys and Renewing Certificates
Why: Regular key and certificate rotation is a security best practice that limits exposure from compromised credentials, and the exam tests whether you understand how AWS automates this. You need to know how automatic KMS key rotation works (annually for customer managed keys), how AWS Secrets Manager automatically rotates database credentials using Lambda functions, and how ACM automatically renews certificates before expiration — reducing operational overhead while improving security.
AWS Documentation:
AWS Service FAQs
- IAM FAQ
- Amazon VPC FAQ
- AWS KMS FAQ
- Amazon S3 FAQ
- AWS Secrets Manager FAQ
- Amazon Cognito FAQ
- AWS Shield FAQ
- AWS WAF FAQ
- Amazon GuardDuty FAQ
- Amazon Macie FAQ
- AWS Certificate Manager FAQ
- AWS Organizations FAQ
- AWS Control Tower FAQ
- AWS Directory Service FAQ
- AWS Direct Connect FAQ
- AWS Backup FAQ
- Amazon EBS FAQ
- Amazon RDS FAQ
- Amazon DynamoDB FAQ
- Elastic Load Balancing FAQ
- Amazon CloudFront FAQ
- AWS Security Hub FAQ
- AWS IAM Identity Center FAQ
- AWS Systems Manager FAQ
- AWS Config FAQ
- AWS Audit Manager FAQ
Final Thoughts
Domain 1 sets the foundation for every other architecture decision on AWS. If you understand identity, access boundaries, and responsibility models, the rest of the exam becomes significantly easier. This study guide is intentionally documentation-heavy because AWS certifications reward architects who understand design intent, not just console workflows — master these concepts, and you’ll not only pass the exam but also design better, more secure systems in the real world.