How to Handle Authentication with Postman API Testing

Postman is a popular tool for API testing, and it provides several features to handle authentication seamlessly during testing .
What is authentication?
Authentication is the process of verifying the identity of a user or system attempting to access a resource, system, or application.
It ensures that the entity requesting access is who or what it claims to be. In the context of computer systems, authentication is a fundamental security measure used to protect sensitive information and resources from unauthorized access.
Authentication typically involves the following steps:Identification:
 The user or system provides a unique identifier, such as a username,
 email address, or account number, to indicate their identity.Verification:
 The system verifies the provided identifier against stored credentials,
 such as passwords, biometric data, cryptographic keys, or security tokens.
Authorization: Once the user's identity is confirmed through authentication,
 the system determines whether the authenticated user has the necessary
permissions and privileges to access the requested resource or perform the
 requested action.
Types of authentication supported by Postman :
Postman supports several types of authentication methods, allowing you to test APIs that require various authentication mechanisms.
Here are the common authentication types supported by Postman:
1 ) . Basic Authentication:
Postman supports Basic Authentication, where the client sends the username and password as part of the request header. This method is commonly used for simple authentication scenarios.
When setting up Basic Authentication in Postman:
Request Setup: Begin by selecting the request you wish to authenticate within the Postman interface.
Authorization Tab: Within the request settings, navigate to the “Authorization” tab.
Select Basic Auth: From the dropdown menu in the “Authorization” tab, choose “Basic Auth” as the authentication type.
Enter Credentials: Postman will prompt you to input the username and password associated with the API you’re testing.
Request Execution: When you execute the request, Postman automatically encodes the provided credentials and adds them to the request header using the Basic Authentication format.
Server Processing: Upon receiving the request, the server extracts the username and password from the Authorization header, decodes them, and validates them against its authentication database.
Response Handling: Depending on the validity of the credentials, the server will either process the request as intended or return an authentication failure response (HTTP status code 401 Unauthorized).
While Basic Authentication offers simplicity, it’s essential to consider its security implications. Since the username and password are sent with each request, it’s crucial to ensure that the communication occurs over a secure connection (such as HTTPS) to prevent unauthorized access.
2 ) . Bearer Token Authentication:
Bearer Token Authentication involves including a token in the request header to authenticate the user. Postman allows you to easily add bearer tokens to your requests.
Here’s a detailed overview of how to use Bearer Token Authentication in Postman:
Obtain the Bearer Token:
Before using Bearer Token Authentication in Postman, you need to obtain the token from the authentication provider or API service you’re testing. This token could be obtained through an OAuth 2.0 authentication flow, an API key exchange, or any other token generation process provided by the API service.
Request Setup:
Select the request you want to authenticate in the Postman interface.
Authorization Tab:
Navigate to the “Authorization” tab within the request settings.
Select Bearer Token:
From the dropdown menu in the “Authorization” tab, choose “Bearer Token” as the authentication type.
Enter Token:
Postman will prompt you to input the bearer token you obtained in the previous step. Paste the token into the provided field.
Request Execution:
When you execute the request, Postman automatically includes the bearer token in the request header using the “Authorization” header field. The token is preceded by the word “Bearer” to indicate the token type.
Server Processing:
Upon receiving the request, the server verifies the bearer token included in the request header. If the token is valid and authorized to access the requested resource, the server processes the request. Otherwise, it returns an authentication failure response (HTTP status code 401 Unauthorized or 403 Forbidden).
3 ). OAuth 1.0a Authentication:
Postman supports OAuth 1.0a, an older version of the OAuth protocol. This method is used for authenticating API requests through token-based authentication.
Here’s a detailed overview of OAuth 1.0a authentication in Postman:
Obtaining OAuth 1.0a Credentials:
Before configuring OAuth 1.0a authentication in Postman, you need to obtain the necessary credentials from the API provider. These credentials typically include a client ID, a client secret, and other parameters required for OAuth 1.0a authentication.
Request Setup:
Select the request you want to authenticate in the Postman interface.
Authorization Tab:
Navigate to the “Authorization” tab within the request settings.
Select OAuth 1.0:
From the dropdown menu in the “Authorization” tab, choose “OAuth 1.0” as the authentication type.
Enter OAuth 1.0a Credentials:
Postman will prompt you to input the OAuth 1.0a credentials you obtained from the API provider. These typically include the consumer key, consumer secret, access token, access token secret, and other optional parameters.
Additional OAuth 1.0a Settings:
Depending on the requirements of the API provider, you may need to configure additional settings such as request token URL, access token URL, and callback URL. These settings are provided by the API provider during the OAuth 1.0a authentication setup.
Request Execution:
When you execute the request, Postman automatically handles the OAuth 1.0a authentication process. It includes the necessary OAuth 1.0a parameters in the request headers, such as the OAuth signature, nonce, and timestamp.
Server Processing:
Upon receiving the request, the server validates the OAuth 1.0a parameters included in the request headers. If the parameters are valid and authorized, the server processes the request and returns the appropriate response.
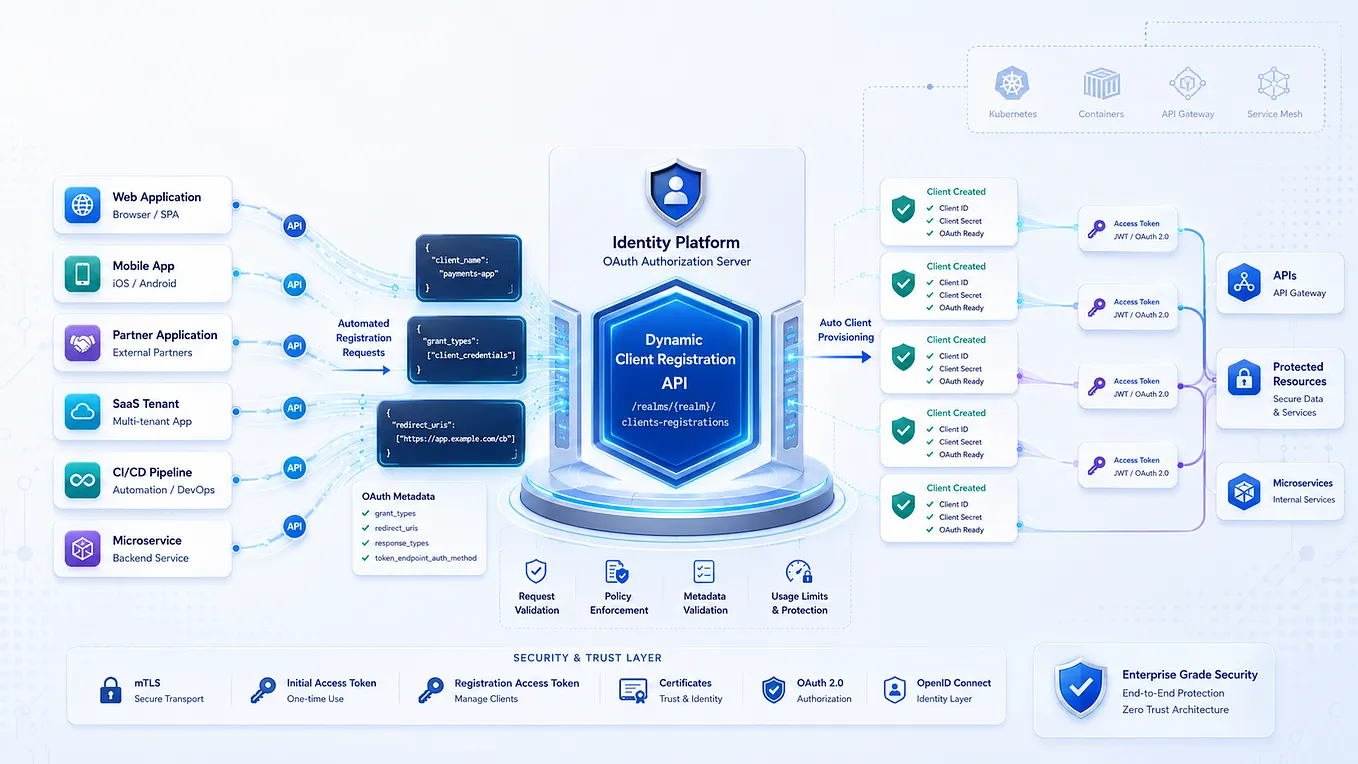
4 ) . OAuth 2.0 Authentication:
Postman provides built-in support for OAuth 2.0 authentication. You can configure Postman to handle OAuth 2.0 flows such as Authorization Code, Implicit, Password, and Client Credentials. Postman can obtain access tokens and handle token refresh automatically.
Here’s a detailed overview of OAuth 2.0 authentication in Postman:
a ). OAuth 2.0 Flows:
OAuth 2.0 defines several authorization flows, each suitable for different scenarios. Postman supports the following OAuth 2.0 flows:
Authorization Code Grant: Used for web server and mobile apps where the client can securely store a client secret.
Implicit Grant: Typically used for single-page web apps or mobile apps where the client can’t securely store a client secret.
Resource Owner Password Credentials Grant: Allows exchanging a user’s credentials (username and password) for an access token. It’s less secure and not recommended for most scenarios.
Client Credentials Grant: Used for machine-to-machine authentication where no user interaction is involved.
b). Request Setup:
Begin by selecting the request you want to authenticate in the Postman interface.
c). Authorization Tab:
Navigate to the “Authorization” tab within the request settings.
d). Select OAuth 2.0:
From the dropdown menu in the “Authorization” tab, choose “OAuth 2.0” as the authentication type.
e ). Configure OAuth 2.0 Settings:
Postman provides a user-friendly interface for configuring OAuth 2.0 settings based on the chosen flow. You’ll typically need to enter the following information:
Authorization URL: The URL where the client initiates the authorization process.
Access Token URL: The URL where the client exchanges an authorization grant for an access token.
Client ID: The unique identifier assigned to the client application by the authorization server.
Client Secret: A secret known only to the client application and the authorization server (required for Authorization Code Grant and Client Credentials Grant).
Scope: The permissions requested by the client application.
Redirect URL (for Authorization Code Grant and Implicit Grant): The URL where the authorization server redirects the user after granting authorization.
Get Daegi_diary’s stories in your inbox
Join Medium for free to get updates from this writer.
Request Execution: When you execute the request, Postman automatically handles the OAuth 2.0 authentication process based on the configured settings. It manages the redirection, token exchange, and token management seamlessly.
f). Token Management:
Postman automatically manages access tokens obtained during the authentication process. It handles token expiration, refresh token flow (if supported), and token storage securely.
5 ). Digest Authentication:
Digest Authentication is a challenge-response authentication mechanism. While Postman doesn’t natively support it, you can use pre-request scripts to manually generate the required headers.
Here’s a detailed overview of how you can implement Digest Authentication in Postman:
Understanding Digest Authentication:
Digest Authentication works by hashing the username, password, and other parameters with a nonce (a server-generated token) to create a digest, which is then included in the request header. The server verifies the digest to authenticate the user.
Pre-request Script Setup:
Begin by selecting the request you want to authenticate in the Postman interface.
Pre-request Script Tab:
Navigate to the “Pre-request Script” tab within the request settings.
Write the Script:
Write a JavaScript script to generate the Digest Authentication header. The script should perform the following steps:
Parse the WWW-Authenticate header from the server response to extract the necessary parameters (nonce, realm, etc.).
Calculate the hash of the username, password, and other parameters using the MD5 hashing algorithm.
Construct the Authorization header with the calculated digest and other parameters required by the Digest Authentication scheme.
Understanding Digest Authentication:
Digest Authentication works by hashing the username, password, and other parameters with a nonce (a server-generated token) to create a digest, which is then included in the request header. The server verifies the digest to authenticate the user.
Pre-request Script Setup:
Begin by selecting the request you want to authenticate in the Postman interface.
Pre-request Script Tab:
Navigate to the “Pre-request Script” tab within the request settings.
Write the Script:
Write a JavaScript script to generate the Digest Authentication header. The script should perform the following steps:
1) Parse the WWW-Authenticate header from the server response to extract the necessary parameters (nonce, realm, etc.).
2) Calculate the hash of the username, password, and other parameters using the MD5 hashing algorithm.
3) Construct the Authorization header with the calculated digest and other parameters required by the Digest Authentication scheme.
Here’s an example of a pre-request script for Digest Authentication in Postman:
JavaScript
const username = 'your_username';
const password = 'your_password';
const realm = 'realm_value'; // Extracted from the WWW-Authenticate header
const nonce = 'nonce_value'; // Extracted from the WWW-Authenticate header
const method = pm.request.method;
const uri = pm.request.url.getPath();
const qop = 'auth';
const ha1 = CryptoJS.MD5(`${username}:${realm}:${password}`).toString(CryptoJS.enc.Hex);
const ha2 = CryptoJS.MD5(`${method}:${uri}`).toString(CryptoJS.enc.Hex);
const response = CryptoJS.MD5(`${ha1}:${nonce}:00000001:${qop}:${ha2}`).toString(CryptoJS.enc.Hex);const authHeader = `Digest username="${username}", realm="${realm}", nonce="${nonce}", uri="${uri}", response="${response}", qop="${qop}", nc="00000001", cnonce="";`;pm.request.headers.add({
key: 'Authorization',
value: authHeader
});
Make sure to replace ‘your_username’, ‘your_password’, ‘realm_value’, and ‘nonce_value’ with the actual values obtained from the server response.
Request Execution:
When you execute the request, Postman will run the pre-request script to generate the Digest Authentication header and include it in the request. The server will verify the header and authenticate the user accordingly.
NTLM(NT LAN Manager) Authentication:
Postman supports NTLM (Windows Integrated Authentication) for APIs that require it. NTLM is a challenge-response authentication protocol used in Windows environments.
Here’s a detailed overview of how you can implement NTLM Authentication in Postman:
Understanding NTLM Authentication:
NTLM Authentication is a challenge-response authentication protocol that involves multiple round-trips between the client and server. It requires the client to authenticate with a domain controller by proving its identity using a cryptographic exchange. The server then validates the client’s identity and grants access to the requested resource.
Pre-request Script Setup:
Begin by selecting the request you want to authenticate in the Postman interface.
Pre-request Script Tab:
Navigate to the “Pre-request Script” tab within the request settings.
Write the Script:
Write a JavaScript script to perform NTLM Authentication. The script should perform the following steps:
1) Send an initial request to the server without authentication to retrieve the NTLM challenge.
2) Extract the NTLM challenge from the server response.
3) Generate the NTLM authentication header based on the challenge, username, password, and domain.
4) Include the NTLM authentication header in subsequent requests to authenticate with the server.
Here’s an example of a pre-request script for NTLM Authentication in Postman:
// Importing the library
const ntlm = require('postman-ntlm-auth');

// Define your NTLM credentials
const credentials = {
    username: 'your_username',
    password: 'your_password',
    domain: 'your_domain', // Optional: Only if required by your NTLM configuration
    workstation: 'your_workstation' // Optional: Only if required by your NTLM configuration
};

// Set up NTLM authentication
ntlm.addNTLMAuthToHeaders(pm.request, credentials);

// Print headers (optional)
console.log(pm.request.headers);
Replace ‘your_username’, ‘your_password’, ‘your_domain’, and ‘https://your_api_endpoint' with the actual values corresponding to your NTLM authentication setup.
Request Execution:
When you execute the request, Postman will run the pre-request script to perform NTLM Authentication. The script will handle the authentication process and include the NTLM authentication header in the request to authenticate with the server.
Hawk Authentication:
Hawk is a HTTP authentication scheme providing a simple way for clients to sign requests with a MAC (Message Authentication Code) and a set of headers. Postman supports Hawk Authentication.
Here’s a detailed overview of how you can implement Hawk Authentication in Postman:
Understanding Hawk Authentication:
Hawk Authentication works by including a cryptographic signature in the request header, along with other parameters such as the user’s identifier and nonce. The server verifies the signature to authenticate the user and authorize the request.
Pre-request Script Setup:
Begin by selecting the request you want to authenticate in the Postman interface.
Pre-request Script Tab:
Navigate to the “Pre-request Script” tab within the request settings.
Write the Script:
Write a JavaScript script to generate the Hawk Authentication header. The script should perform the following steps:
Generate a nonce (a unique value) to prevent replay attacks.
Calculate the timestamp of the request.
Construct the Hawk Authorization header with the necessary parameters such as the user’s identifier, timestamp, nonce, and signature.
Include the Hawk Authorization header in the request
Here’s an example of a pre-request script for Hawk Authentication in Postman:
JavaScript
const Hawk = require('hawk');
const credentials = {
    id: 'your_user_id',
    key: 'your_shared_secret',
    algorithm: 'sha256'
};
const timestamp = Math.floor(Date.now() / 1000);
const nonce = Hawk.utils.randomString(6);const request = {
method: pm.request.method,
host: pm.request.url.getHost(),
port: pm.request.url.getPort() || (pm.request.url.protocol === 'https' ? 443 : 80),
resource: pm.request.url.getPath(),
headers: {
'Host': pm.request.url.getHost(),
'Timestamp': timestamp,
'Nonce': nonce
}
};const header = Hawk.client.header(pm.request.url.toString(), pm.request.method, { credentials: credentials, ext: 'your_optional_payload' });
pm.request.headers.add({
key: 'Authorization',
value: header.field
});
These were all possible authentication methods in postman . Hope it helped
Please do follow for more such content that means a lot .
Byee byeeeeee
Take care 💜👋