Anuragshah·Sep 28Where to Start Ethical Hacking? A Beginner’s RoadmapMost people who ask where to start ethical hacking are stuck on the same thing. They search for it, find a hundred tool lists and a dozen…
Yunis Ahmadli·Sep 7TryHackMe: CTF collection Vol.1 walkthroughHello, This room is easy and 45 minutes CTF room in TryHackMe. So, let’s get started without extending the beginning.A response icon1A response icon1
CYBER MIND SPACE·Aug 28SQL Injection in 2026: Why It Still Exists and Where Developers Get It WrongSQLi has been in the OWASP Top 10 since the list existed. It’s older than most bug bounty programs. Every bootcamp teaches “use…
Arturo Cannarozzo·Aug 21Beyond the "Black Hat" Myth: Why Hackers and Organized Cybercriminals Are Not the SamePhoto by Luther.M.E. Bottrill on Unsplash
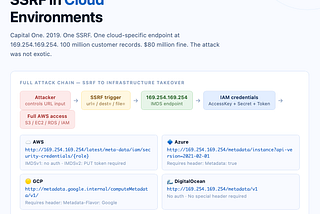
CYBER MIND SPACE·Aug 17SSRF in Cloud Environments: Metadata Services, Trust Boundaries, and MitigationsCapital One. 2019. One SSRF. One endpoint at 169.254.169.254. 100 million customer records. $80 million fine. The attack was not exotic…
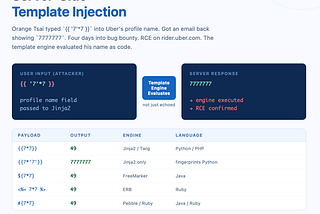
CYBER MIND SPACE·Aug 14Server-Side Template Injection: Detection Mindset and Safe Lab AnalysisMost hunters treat SSTI like a copy-paste payload race — throw {{7*7}}, see 49, scream RCE, move on. That's not hunting, that's pattern…
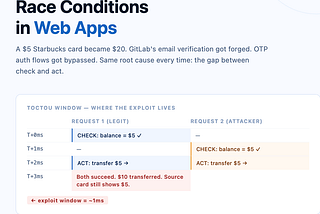
CYBER MIND SPACE·Aug 8Race Conditions in Web Applications: Why Timing Bugs Become Security BugsStarbucks. 2015. Three $5 gift cards. One researcher. And a server that couldn’t keep up with itself.
CYBER MIND SPACE·Aug 6OAuth 2.0 Attack Surface: Redirect URIs, Token Leakage, and Account Takeover RisksApple paid $100,000 for this one. The researcher found it in an afternoon. The server issued OAuth tokens for any email address you asked…
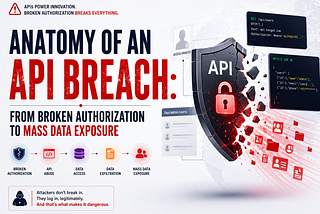
CYBER MIND SPACE·Jul 30Anatomy of an API Breach: From Broken Authorization to Mass Data Exposure207,000 users. bcrypt password hashes. 2FA secrets. Password reset tokens. One API endpoint. No exploit required.