fmi A.·1d agoWhat Happens After the Cybersecurity Checklist?The questions are answered. The spreadsheet is complete. But who makes the decisions?
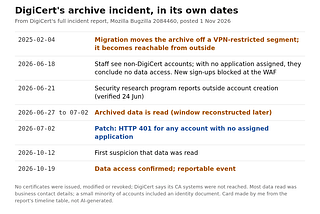
Josepollman·3d agoDigiCert Moved an Internal Archive to a Reachable Network and Treated It as an Infrastructure ChangeDigiCert says archived customer data, including a few ID documents, was read 27 June to 2 July. No certificates were touched.
Fiona Chan·Oct 27AI Reads the Document. The Practitioner Reads the Room.There’s a genre of LinkedIn post that privacy, data governance, and AI governance professionals will recognise immediately. A vendor CEO…
Mr.PlanB·Oct 22What Is Vendor Billing Compliance?Vendor billing compliance checks whether supplier invoices reflect authorized work, actual delivery, agreed pricing, approved budgets, and…
Saurav Tripati·Oct 21AI Third-Party Risk Management Means Tracking Model Provenance TooA vendor can pass every questionnaire truthfully and still be the weakest link in an AI supply chain. AI third party risk management closes…A response icon1A response icon1
Monaf Elsayed·Oct 20How to Run Vendor Due Diligence: 8 Risk Categories, 6 Deal-Breakers and a Simple Scoring ModelA practical framework any procurement, compliance or finance team can apply, with or without expensive software.
Agron Fazliu·Oct 17When one supplier holds the keysSmall organizations often have very capable technology suppliers. A family office may work with the same provider for years because the…
Tyson Martin·Oct 15The vendor contract that can change your sale priceSomewhere in your company is a contract nobody has read in years. In a sale, it can matter more than almost anything on your technology…
Mr.PlanB·Oct 11A Grammarly Cancellation Sparked an Employee Email StormOne IT team’s account of unwanted renewal messages shows why contacting employees behind the buyer’s back can destroy enterprise trust.