Gabriel Odusanya·Sep 30How I Built a GitHub Actions Pipeline for OWASP A02 Security Misconfiguration1. Introduction
Gabriel Odusanya·Sep 25File Uploads Still Lead to RCE — What I Learned Breaking Avatar Upload on PortSwiggerFile upload looks harmless. “Just let users set a profile picture.” That one feature is still one of the most common ways a web app hands…
Jessica·Sep 16SQL Injection: A Beginner’s GuideSQL Injection sounded complicated to me when I first started learning web security. I didn’t understand why some random characters could…
Jessica·Sep 13Stored Cross-Site-Scripting(XSS): A Beginner’s GuideI want you to checkout my previous blog on XSS before jumping into Stored XSS. Do not miss out the links embedded within words!
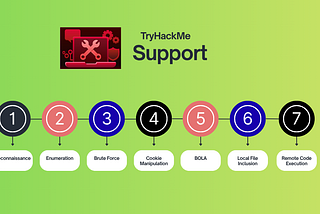
S4F4L·Sep 12Support Challenge — TryHackMe WalkthroughPentest the Support Ops platform to exploit vulnerabilities and achieve RCE.
Chavanamit·Aug 30🔓 How I Bypassed an SSRF Filter Using an IPv6 AddressHow an “unallowed” localhost became reachable just by writing it differently 🕵️♂️A response icon1A response icon1
Nina Wagner·Aug 18The Basics of Web VulnerabilitiesTaking control of systems, bypassing approval processes, and financial damage from lost revenue — these are just some of the possible…
Amna Lodhi·Aug 17Lab: Server-side pause-based request smugglingWhat Is Server-Side Pause-Based Desync
Sebastian Vargas·Aug 162 Race Condition let me get money free on a 10 Million users Company on a Hackerone programHello everyone, Today, I want to share two interesting race condition vulnerabilities that I discovered in a vulnerability disclosure…